On This Page
TCPA and AI Texting: Consent, Opt-Outs, and Automation Guardrails
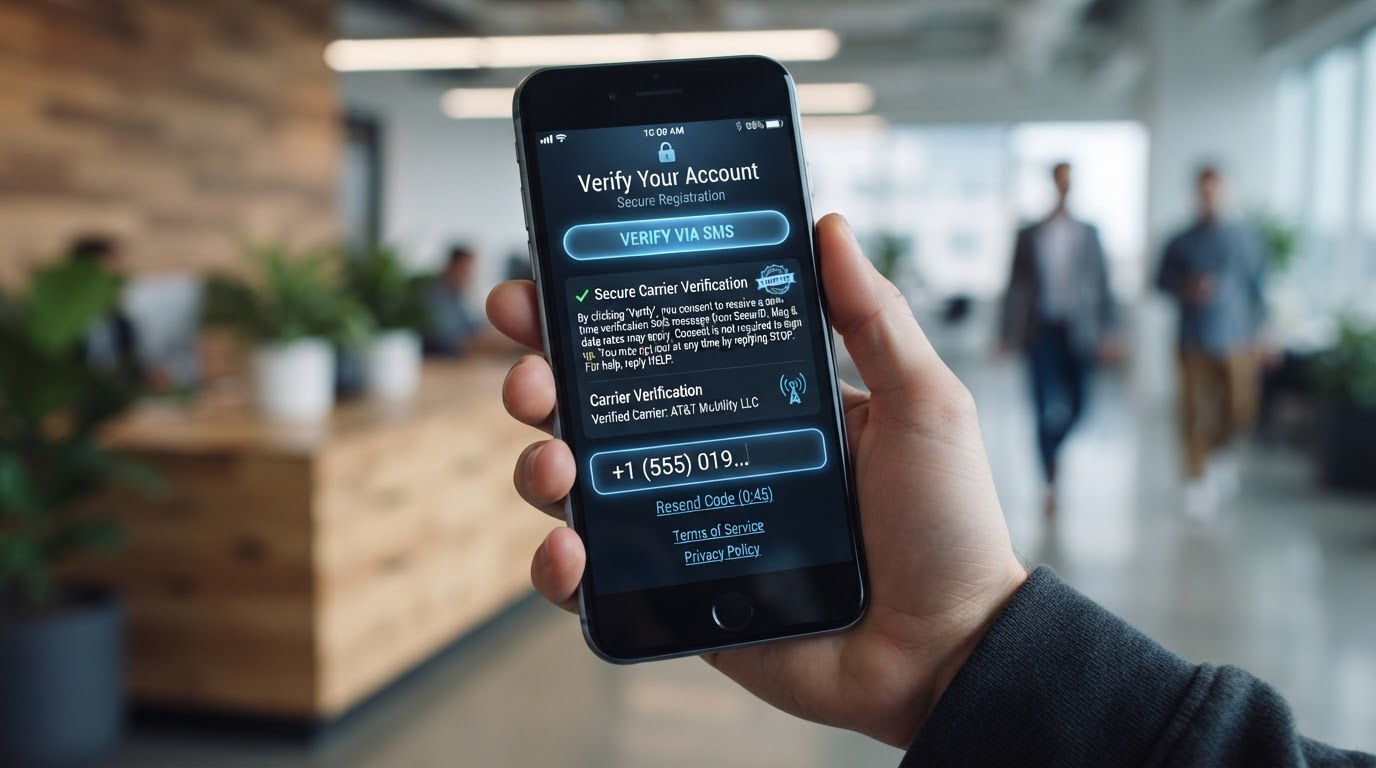
Automated texting is one of the highest-ROI channels for service businesses — but it's also one of the most regulated. The Telephone Consumer Protection Act (TCPA) governs how businesses can send automated SMS, and the penalties for violations are severe: $500–$1,500 per text, per recipient, which means a single campaign sent to 1,000 recipients without proper consent can generate a $500,000–$1.5M liability. The good news is that compliance is achievable — it just requires understanding what consent you need, how to handle opt-outs, and what guardrails to build into your automation. This guide is a plain-English walkthrough of TCPA compliance for AI-powered texting, covering the consent requirements, opt-out handling, the 2024 A2P 10DLC rules, and the practical guardrails that let you use automated SMS without creating legal exposure.
01What the TCPA Actually Requires
The TCPA regulates automated telephone communications, including SMS. The core requirements for automated texting: (1) prior express consent from the recipient before sending automated marketing texts; (2) a clear opt-out mechanism in every message; (3) honoring opt-out requests promptly (within 10 business days, per FCC rules); (4) restrictions on sending times (no texts before 8am or after 9pm local time); (5) accurate sender identification (no spoofed or misleading caller IDs).
The distinction between transactional and marketing texts is critical. Transactional texts — responding to a customer's inquiry, confirming an appointment, sending a receipt — generally do not require prior express consent because they're in response to the customer's action. Marketing texts — promotional messages, upsell offers, newsletters sent to non-customers — require prior express written consent. The missed-call text-back automation framework covers this distinction: a text-back in response to a missed call is transactional (the customer called you); a follow-up marketing sequence to that same customer requires their prior consent.
The safest approach is to treat consent conservatively. Even for texts that might qualify as transactional, obtaining explicit consent — via a checkbox on your form ('I consent to receive text messages') — eliminates the ambiguity and protects against claims that the text was unsolicited. The cost of adding a consent checkbox is zero; the cost of a TCPA claim for an unsolicited text is $500–$1,500 per text. According to the FCC's TCPA compliance guide, the burden of proving consent is on the sender — meaning you need to be able to produce, for every text you send, evidence that the recipient consented. This is why consent logging (discussed below) is non-negotiable.
02Consent: What You Need and How to Capture It
For marketing texts, prior express written consent is required. This means the recipient must explicitly agree — in writing (which includes digital forms and checkboxes) — to receive marketing texts. A pre-checked checkbox does not count; the recipient must actively opt in. The consent form must clearly state what the recipient is agreeing to ('I consent to receive marketing text messages from [business] at the number provided') and must be logged with a timestamp, the recipient's number, and the form submission data.
The consent must be specific to the channel. Consent to receive email does not extend to SMS; consent to receive SMS does not extend to calls. Each channel requires its own consent. If your form asks for both email and SMS consent, use separate checkboxes — one for each channel — so the recipient can opt into one without the other. This specificity is what makes the consent legally valid; bundled consent ('I consent to all communications') is weaker and more likely to be challenged.
Consent can be revoked at any time. The recipient must be able to opt out as easily as they opted in — typically by replying 'STOP' to any message. The opt-out must be honored within 10 business days (per FCC rules), but best practice is to honor it immediately — within seconds — via automated processing. The HIPAA patient intake automation guide covers the same opt-out mechanism for healthcare — the principles are identical for any industry using automated SMS. Log every consent and every opt-out. For every text you send, you should be able to produce: the recipient's consent record (when, how, what form), the consent timestamp, and confirmation that no opt-out was received before the text was sent. This audit trail is your defense if a claim arises.
03Opt-Out Handling: The STOP Command and Beyond
Every automated text must include a clear opt-out mechanism. The industry standard is 'Reply STOP to unsubscribe' — but the mechanism should also handle 'STOP', 'STOPALL', 'UNSUBSCRIBE', 'CANCEL', 'END', and 'QUIT' (all common variations that carriers recognize). When the system receives any of these, it must: (1) immediately add the number to the opt-out list, (2) stop all future texts to that number, (3) send a confirmation ('You've been unsubscribed. Reply HELP for help.'), and (4) log the opt-out with a timestamp.
The opt-out must be respected across all campaigns. A recipient who opts out of one SMS sequence should not receive texts from another sequence — the opt-out is per-number, not per-campaign. This requires a centralized opt-out list that all texting workflows check before sending. The architecture: a 'do-not-text' list in your CRM or texting platform that every SMS workflow queries before sending. If the number is on the list, the text is suppressed. This centralized check is the guardrail that prevents a recipient from being re-texted after opting out — a common compliance gap when multiple workflows operate independently.
The HELP command is also required. Carriers require that automated texting numbers respond to 'HELP' with information about the program: the business name, how to get support, and a reminder of the opt-out mechanism. This is a technical requirement — if your texting number doesn't respond to HELP, carriers may block your messages. The workflow and integration automation service configures these HELP and STOP handlers as a standard part of any SMS deployment.
04A2P 10DLC: The 2024 Rules That Changed Everything
A2P 10DLC (Application-to-Person 10-Digit Long Code) is the regulatory framework that governs how businesses send automated texts via standard phone numbers (not short codes). Implemented fully in 2024, it requires businesses to register their texting numbers with carriers, provide use-case details, and pay per-message fees. The goal is to reduce spam and give consumers more control — but for businesses, it adds a registration and compliance layer.
The key requirements: (1) Register your business and texting use case with a campaign registry (your SMS provider typically handles this). (2) Use only registered numbers for automated texting — unregistered numbers will be blocked by carriers. (3) Pay per-message fees (typically $0.005–$0.01 per message, depending on the use case). (4) Maintain a use-case-appropriate message volume (carriers limit throughput based on the registered use case). (5) Monitor for carrier filtering — if your messages are being filtered, your registration may need adjustment.
The practical impact: businesses that don't register will see their automated texts blocked entirely — the messages won't be delivered, and the business won't know why (carriers don't always notify on filtering). This is why working with an SMS provider that handles A2P 10DLC registration (Twilio, most major platforms) is essential — they navigate the registration and ensure your messages are delivered. According to Twilio's A2P 10DLC guide, businesses that register properly see delivery rates above 95%, while unregistered numbers see delivery rates below 30% — the difference between a working SMS channel and a broken one. The CRM migration checklist guide is relevant if you're moving to a new CRM or SMS provider — the A2P registration must be updated or the messages will stop delivering.
05Guardrails for AI-Powered Texting
When AI generates the text content — a personalized follow-up, a nurture message, a response to a customer inquiry — additional guardrails are needed. The AI must not send marketing content without consent. Even if the AI is generating a 'helpful' message that includes a promotional offer, the offer is marketing — and sending it to a non-consenting recipient is a TCPA violation. The guardrail: the AI's message generation must be constrained to the consented content type. If the recipient consented to transactional texts only, the AI must not include marketing content, even if it's 'relevant' or 'helpful.'
The AI must not text numbers on the opt-out list. This is a technical guardrail, not a policy one: the AI's texting integration must check the do-not-text list before sending, and suppress any message to a listed number. The risk is that an AI workflow — especially one that generates messages dynamically — might bypass the centralized opt-out check if it's not architected correctly. The architecture: all AI-generated texts go through the same SMS gateway that enforces the opt-out check, so the AI cannot send to opted-out numbers even if it tries.
The AI must respect texting hours. No automated texts before 8am or after 9pm local time — and 'local time' means the recipient's local time, not the sender's. If your AI sends a text at 8pm Pacific to a recipient in Eastern time, it's 11pm their time — a TCPA violation. The guardrail: the texting system must determine the recipient's timezone (from their phone number's area code or a stored timezone field) and schedule the text within the permitted window. The lead response time automation framework covers the timing logic — for compliance, the timing must be recipient-aware, not sender-aware.
06Building the Compliance Layer
TCPA compliance is not a single feature — it's a layer that spans your entire texting stack. The components: (1) a consent capture mechanism (the checkbox on your forms) that logs every consent with a timestamp and the form data; (2) a centralized opt-out list that every texting workflow checks before sending; (3) an SMS gateway that enforces the opt-out check, the texting hours, and the A2P registration; (4) an audit log that records every text sent, to whom, with what consent basis, and whether the recipient had opted out; (5) a HELP/STOP handler that responds to carrier-required keywords.
The audit log is the most important and the most often missed. If a claim arises, you need to produce — for every text you sent to the claimant — evidence that they consented, that they hadn't opted out, and that the text complied with the timing rules. Without a centralized audit log, you can't produce this evidence, and the default judgment (in many TCPA cases) goes against the sender. The log should capture: recipient number, message content, timestamp, consent basis (which form, when), opt-out status at send time, and the A2P campaign ID.
The compliance layer should be built before the first text is sent, not after. Retrofitting compliance onto an existing texting system is expensive and error-prone — it's far easier to build the consent capture, opt-out list, audit log, and HELP/STOP handler as part of the initial deployment. The automation audit and consulting engagement includes a compliance review as a standard phase — because a texting automation that isn't TCPA-compliant is a liability, not an asset. The business processes to automate before hiring framework helps identify which texting use cases are worth the compliance investment — because not every business process needs automated SMS, and the ones that do need to be done right.
Key Takeaways
- TCPA requires prior express consent for marketing texts, clear opt-out mechanisms, texting-hour restrictions (8am–9pm recipient local time), and accurate sender ID.
- Capture consent per channel with an unchecked checkbox, log it with a timestamp and form data, and treat consent as revocable at any time via STOP.
- A2P 10DLC requires business and use-case registration with carriers — unregistered numbers see delivery rates below 30%, registered numbers above 95%.
- AI-generated texts must be constrained to consented content types, must check the opt-out list, and must respect recipient-local texting hours.
- Build the compliance layer (consent capture, opt-out list, audit log, HELP/STOP handler) before the first text is sent — retrofitting compliance is expensive and error-prone.
Written by Moise
Founder & Lead Automation ArchitectMoise is the founder and lead automation architect at Wootomatic. With over a decade of hands-on experience designing, implementing, and maintaining high-throughput business automations, CRM pipelines, and custom AI agents, he has architected mission-critical workflows for hundreds of appointment-based and field-service businesses. His focus is on resilient, monitored systems that produce measurable ROI without fragile software bloat.
Ready to Put This Into Action?
Tell us about your workflow and we'll scope a custom automation within 24 hours.
Start Your Automation Project